Information Security and Privacy Protection Management Framework
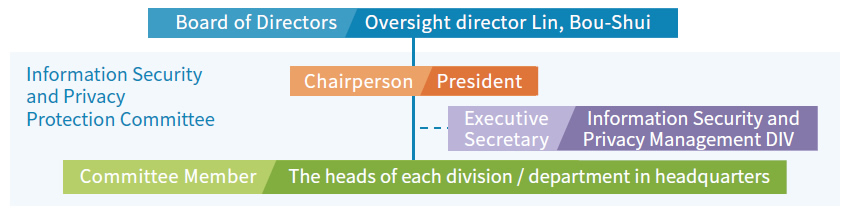
EVA Air has been dedicated to establishing information security systems and complying with legal and regulatory requirements. To ensure independent oversight and checks in information security governance, the “Information Security and Privacy Management Division “is responsible for the management and supervision of information security and personal data protection. Additionally, through the establishment of the “Information Security and Privacy Protection Committee”, our goal is to appropriately balance risk management with business development.
Information Security and Privacy Management Division
The Information Security and Privacy Management Division is responsible for formulating information security and personal data protection policies, promoting regulatory compliance, operating the Information Security Management System and Personal Data Management System, preventing and responding to information security incidents, and planning and delivering awareness and training programs. The Division works with responsible business units to implement these policies, develop operating procedures tailored to their respective functions, and strengthen the information security management framework through performance evaluations. The Division is headed by the Chief Information Security Officer (CISO), who oversees the implementation of information security policies and resource allocation, and reports annually to the Board of Directors on information security governance performance and future plans.
Information Security and Privacy Protection Committee
EVA Air established the Information Security and Privacy Protection Committee in 2022. Chaired by the President, the Committee meets semi-annually. Through the participation of senior management and department heads, the Committee reviews information security and personal data protection policies, strategic development plans, and implementation performance to strengthen information security governance and ensure effective implementation of related policies. The Committee maintains information security resilience and the effective operation of personal data protection management to safeguard the confidentiality, integrity, and availability of information assets, thereby fulfilling the Company's corporate social responsibility and supporting its long-term sustainable development.
Information Security Policy
EVA Air has formulated our information security policy to ensure the confidentiality, integrity and availability of information assets, and prevent internal and external threat whether it’s intentional or not. All personnel of the Company, business related suppliers with its employees, temporary employees, etc., shall abide the rules and procedures of the policy and relevant management mechanisms. The policy is disclosed on the official website to demonstrate the Company’s commitment to upholding information security and personal privacy protection.
EVA Air Information Security Policy
Information Security Management System
EVA Air established our Information Security Management System in accordance with the ISO 27001 international standards. The scope of verification covers areas such as flight safety, aviation security, core passenger and cargo service functions, personal data, and information infrastructure. At least one internal information security audit is conducted annually, focusing on independent verification of policy implementation and control mechanisms. Specific recommendations for improvement are provided based on audit findings. The responsible departments are required to complete necessary adjustments within a specified timeframe. Follow-up reports are submitted to ensure effective implementation and continuous improvement of the management system.
Through verification by the British Standards Institution (BSI) and regular monitoring and review, we ensure the effectiveness of this system. Our current certification is valid from May 13, 2025, to May 12, 2028.
(
ISO 27001_2025、
ISO 27001_2028)
Information Security and Privacy Protection Education, Training and Effectiveness
In order to establish basic information security mindset in employees and enhance their information security awareness, and mitigate information security incidents and its associated impact, we conduct social engineering drill and awareness training for all units both at home and abroad.
Relevant news or information is shared on the Company website regularly. In addition, the Company provides annual information security training for all employees as well as role-specific training for designated personnel. The implementation results for 2025 are summarized in the table below.
All employee
Number of people completed the training(Note) 11,735 person
Training hours2 hours
Coverage rate 100 %
New employee
Number of people completed the training 1,197 person
Training hours1 hours
Coverage rate 100 %
Information technology personnel
Number of people completed the training 295 person
Training hours2 hours
Coverage rate 100 %
Information security personnel
Number of people completed the training 7 person
Training hours12 hours
Coverage rate 100 %
Reporting Channel and Procedure for Employees
Employees who identify an information security incident are required to report it immediately in accordance with established procedures. Outside headquarters' business hours, incidents are reported through the emergency hotline. Upon receiving a report, the Information Security and Privacy Management Division determines whether the case constitutes an information security incident and reports it to the Chief Information Security Officer (CISO). Based on the preliminary severity assessment, the Information Security Operations Coordination Meeting determines whether to activate the incident response procedures. Relevant departments are then convened to report the incident status, implement response measures, and develop appropriate solutions.
Information security incident drills cover two categories: personal data breaches and cybersecurity incidents. At least six drills are conducted annually to ensure that responsible departments can promptly obtain incident information through the reporting process, assess the situation, and implement necessary response measures to minimize impacts. The drills also validate the effectiveness of the incident response procedures, strengthen employees' information security awareness and response capabilities, and enhance cross-departmental coordination.
Employees who violate information security policies or the Company's rules governing the use of electronic information systems are subject to disciplinary action in accordance with the Employee Management Rules, depending on the severity of the violation.
Privacy and Personal Data Protection
While providing customer services, EVA Air is committed to protecting customers' personal data, privacy, and rights. The collection, processing, and use of personal data comply with the Personal Data Protection Act, the EU General Data Protection Regulation (
GDPR), the California Privacy Rights Act (CPRA), and other applicable privacy laws in the jurisdictions where EVA Air operates. These commitments are set out in the Company's
EVA Air’s Privacy Policy &
Cookies Terms and Conditions on the EVA Air website.
All employees, employees of vendors and their temporary employees, and others with business dealings with the Company are required to comply with these requirements to minimize the risk of unauthorized access, alteration, loss, damage, or disclosure of personal data.
Privacy Information Management System
EVA Air has established a Privacy Information Management System (PIMS) in accordance with
ISO 27701, with the personal data of passengers, Infinity MileageLands members, and customers included within the certification scope of both ISO 27701 and ISO 27001. At least one internal personal data protection audit is conducted annually to independently assess control measures, with corrective actions and follow-up implemented to support continual improvement. The PIMS has been certified by the British Standards Institution (BSI), with certification valid from May 13, 2025, to May 12, 2028, consistent with the Information Security Management System certification period.